Ady Stokes
Ady Stokes
Freelance Consultant
He / Him
MoT Ambassador. Currently semi-retired and freelancing. I am, amongst other things, a writer, speaker, and accessibility advocate. Leeds Chapter Lead. MoT Certs curator and article editor for WonderProxy. Testing wisdom, friendly, testing songs and poems. Great minds think differently. STEC and SQEC Certified. Struggling to write a book about testing mindsets and thinking's application in software development.
🎂 MoTaBirthday | March 11, 2017
Open To
Teach
Speak
Podcasting
Review Conference Proposals
Write
Meet at MoTaCon 2027
At TWiQ, I mentioned how I managed to get multiple teams doing demonstrations for each other to make work more visible. One team found that another team had solved their problem and learned from th...
23 Oct
Something cool happened? Noticed a glitch in the matrix in live? (See Louise spelling mistakes) Heard a cool point made in This Week in Testing? Dog sitting. See a duck, real or rubber. Doesn't mat...
23 Oct
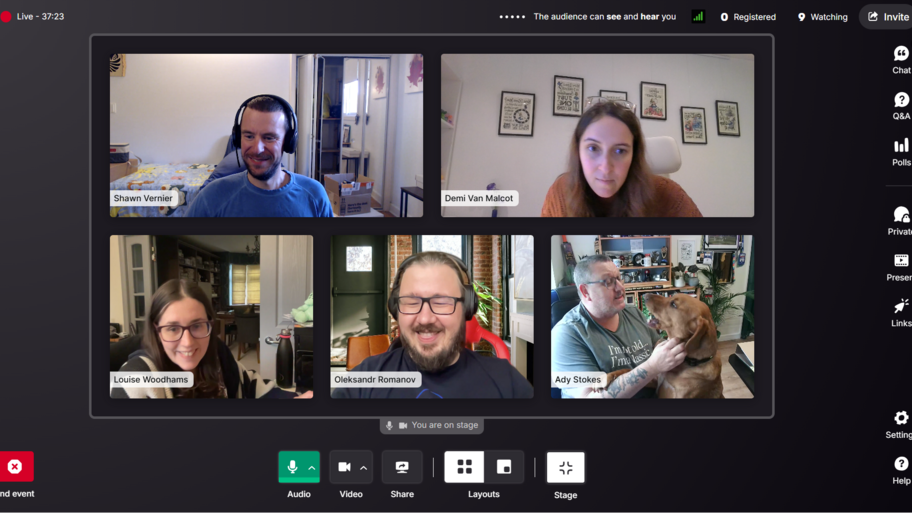
Ady Stokes is dogsitting this week on the paw-rific Dexter. The canine joined us live on stage during This Week in Quality!
23 Oct
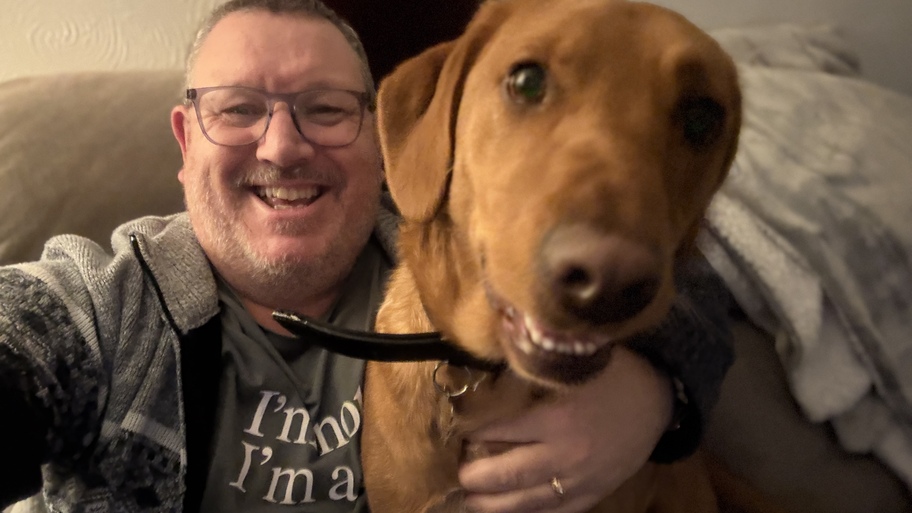
Pupdate. A new VIP has joined us for a week or so. That's Very Important Pet in case you didn't know. Dexter is a two year old Labrador cross, not sure what with. He is still in the puppy phas...
23 Oct
Modernise your design strategy with mobile-first and keyboard-centric approaches that create more resilient, accessible, and user-friendly software.
5 Mar
The gang explore security vulnerabilities, the challenges of testing randomness and AI, and how better communication and collaboration can strengthen quality across teams.
23 Oct
Watch the world-famous rapid-fire 99 Second Talks delivered by various attendees at MoTaCon 2026.
20 Oct
Clickjacking
Clickjacking is a cyberattack where a malicious attacker tricks an authenticated user by placing a transparent layer over a link or button to take you to a fake site embedded inside the real one or to authorise an action that could cause you harm.
SWOT Analysis
Strengths, Weaknesses, Opportunities, Threats (SWOT). Four boxes, often in a grid. Can be used individually or for teams. I'd guess some of you have sat through a workshop where someone's drawn it on a whiteboard or handed out sheets, excited to discover root causes, gaps and productivity gains. So why does it so often end up as a box-ticking exercise, particularly for teams, rather than something genuinely useful? If it isn't familiar to you, you may have done something similar with 'What's going well, what's going wrong, and what could be better?' That and similar exercises are essentially watered-down versions of the original SWOT that came from the Stanford Research Institute in the 1960s.
Strengths and Weaknesses look inward. What are we good at, and where do we fall down? Opportunities and Threats look outward, at the world beyond the team or the product. That split matters more than it gets credit for. It's easy to fill the grid with things you already believe about yourself and never actually look deep inside. I'm the same. One done for me looks very different to one done as part of a team.
I've sat in sessions where the "weaknesses" box got suspiciously thin because nobody wanted to be the one writing something uncomfortable down in front of the boss. No one likes admitting weakness. No one likes openly criticising or questioning colleagues. But that's not a SWOT problem. That's a psychological safety problem.
In my opinion, it earns its keep first when you are honest, and then when it is used as a starting point for conversation rather than just an answer. Whatever is captured is worth nothing unless it is the truth, and until someone asks what we're actually going to do with that information.
Work in progress (WIP) and limits
Work in progress, or WIP, means exactly what it says. Work that's in progress. Started, not finished, sat somewhere in the middle. Simple enough, in theory. But there's more to it than that.
Where it gets interesting, or annoying, depending on your team, is WIP limits. That's a deliberate cap on how many things can be "in progress" at once, originating from Kanban and lean manufacturing. In my experience, most teams have a WIP problem because everyone's trying to help, everyone picks something up, and suddenly there are fourteen tickets half-finished and nothing actually shipped. Because busy isn't the same as done, is it?
A WIP limit forces a choice. Finish this thing, or you can't move on. I can't remember when I came across the saying "stop starting, start finishing". I believe it is an Agile principle, or it was originally linked to Kanban, but I'm not sure. What I do know is that for a long time I had a post-it note on my desk with it on, and it helped me focus on the work in front of me.
So next time your board's heaving with WIP, don't just ask what's blocked. Ask why so much got started in the first place and how we can improve the process.
Two Factor Authentication (2FA)
Two factor authentication, or 2FA, is a security process where a user provides two distinct forms of identification before gaining access to an account, system, or application.
In identity and access management (IAM) architectures, 2FA acts as a security gate within the authentication workflow, enforcing multi-layered defence.Authentication Factors look to combine two distinct pieces of information.
A knowledge Factor, which could be passwords, PINs, or secret answers.
A possession Factor, such as One Time Passcode (OTP), secondary apps e.g., Google Authenticator, Authy, etc.
An Inherence Factor is something you are. Your biometric data for Face ID, a fingerprint scanner, or even iris scans for secret agents or super villains!
For testing, you can mock 2FA endpoints in non-production environments to avoid dependencies on third parties. In automation, secret keys can work in test environments to generate valid OTP tokens within end-to-end UI tests. You can also implement conditional test configurations or feature flags (e.g., test-only OTPs or environment-level 2FA bypass) specifically for CI/CD pipeline runs.
OTP (One Time Passcode)
An OTP is an automatically generated and secure numeric or alphanumeric string of characters that authenticates a user for a single transaction or login session.
Unlike the usual run of the mill passwords you use to log in to a site or app, an OTP (One Time Passcode) is valid for one use only. They are sent to previously provided details such as a phone number or email address. They typically expire after a short duration. Something like 1 to 5 minutes is typical, but some can be 10 minutes. It serves as a second layer of defence in Two Factor Authentication (2FA) and Multi Factor Authentication (MFA). They can also come from authentication apps or be physical hardware tokens.
Comments
(175)
Spelling mistakes in the wild!
Personally, I'd be very wary of a spam site with that spelling.
Customer parking only
I need to get out more or be more observant when I am. You see the coolest things.
Make it joyful: How to build products that make people smile
Loved this, thank you, Clare
99 Seconds at MoTaCon 2026
I love Rich Adams poem. Thank you to all 99-second talkers and to the audience for clapping along with my nonsense
Ady asks #5 Mindset chapter draft updated after feedback
Thank you Lisa. The repetition is deliberate but I take your point about the longer paragraphs. There is a chapter I might share called, ‘Who on Earth is Ady Stokes’ where I share my journey into software testing and becoming an accessibility advocate.
22 Oct
Learner finished your session
PHP Dramas, DOG Dexter and BIG Buttons
Community Star
about 6 hours ago
Thanks for your contribution
PHP Dramas, DOG Dexter and BIG Buttons
Community Star
about 6 hours ago
Learner completed your lesson
8.8.0 of MoT Software Quality Engineering Certificate
Community Star
about 6 hours ago
